Microsoft Learn
Free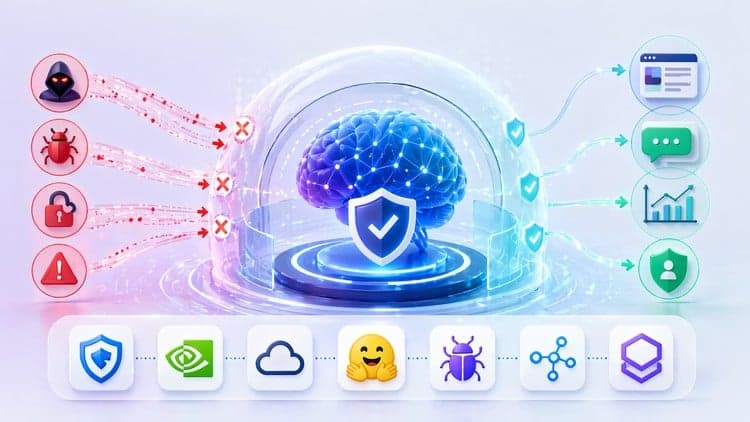
Price
No active coupon right now
View Course →No coupon right now. We'll tell you when there is one.
Mark your own learning status. Opening a course link does not establish enrollment.
Loading saved status…
The course traces a request through a GenAI application and tests the guardrails at each point: input, output and data. It is built to make failure modes concrete, starting with the chatbot incidents that tend to reach the news.
Later modules move into agents: an AI pentest agent built with CrewAI and OWASP ZAP, plus the top risks for agentic applications that OWASP has catalogued. A capstone assessment closes the course.
Updated in 2026
The course has been re-recorded and reorganized into a clear six-part path, based on feedback from thousands of students. New content includes Microsoft Presidio, Penn Testing AI Agent and OWASP Top 10 for Agentic Applications.
Your GenAI app will be attacked. Will your guardrails hold?
In IBM's 2025 Cost of a Data Breach report, 13% of organizations reported a breach involving an AI model or application, and 97% of those had no proper AI access controls. Chatbots have been talked into selling a car for $1, a parcel-delivery bot was coaxed into swearing at its customers, and an airline was held liable for what its chatbot invented. This course teaches you to prevent those failures, step by step and hands-on.
How the course is organized
The course follows the path of a request through a GenAI application, tests and hardens its guardrails, then shows how to build and secure AI agents. Every part builds on the one before:
Foundations. How LLMs, inference parameters, embeddings, RAG and prompts work, and the risks they create, mapped to the OWASP Top 10.
Defend the pipeline
Input: stop prompt injection with Prompt Guard and Llama Guard, including attacks hidden in images (Llama Guard 3 Vision). OWASP LLM01.
Output: detect hallucinations with judge models and Vectara's evaluation model. OWASP LLM09.
Data: find and anonymize PII with Microsoft Presidio. OWASP LLM02.
Test. Prove your guardrails work with faithfulness, SAS and context-relevance evaluators and a full RAG evaluation in Haystack, then red-team the model with Garak (encoding, data exfiltration and profanity probes).
Build. Combine defenses with GuardrailsAI (validators, RAIL, on-fail policies) and NVIDIA NeMo Guardrails (Colang, runtime), then do the same with managed Amazon Bedrock Guardrails and Bedrock evaluations.
AI agents. Build an AI pentest agent with CrewAI and OWASP ZAP, then a bonus multimodal ReAct agent, and learn how agents connect to tools through MCP.
Secure agentic AI. Work through all ten risks in the OWASP Top 10 for Agentic Applications (2026), from Agent Goal Hijack to Rogue Agents. Each risk comes with real-world scenarios, a technology map, a defense architecture and a knowledge check, and the course ends with a capstone assessment.
What you'll get
Hands-on labs with open-source models from Hugging Face, in Google Colab
A section recap at the end of every core section, and knowledge checks throughout
Downloadable slides and notebooks (confirm they're attached before you claim this)
A one-page guardrails playbook to take back to your team
Advertisement
Tracking since 15 Nov — not enough history yet to tell you whether today's price is any good. Watch the course and we'll tell you when it drops.
This is what we recorded in US pricing — not every price this course has ever had, and prices differ by country.
No Korshub reviews yet.